
AI is now part of everyday business. Companies use it for writing, customer support, coding, research, marketing, finance, data analysis, and many other tasks.
Using one AI tool can be simple. Using AI across a whole company is much harder. Once AI can access company data, help make decisions, or take actions, businesses need clear rules.
Who controls the AI? What data can it use? Who checks its work? Who is responsible when something goes wrong?
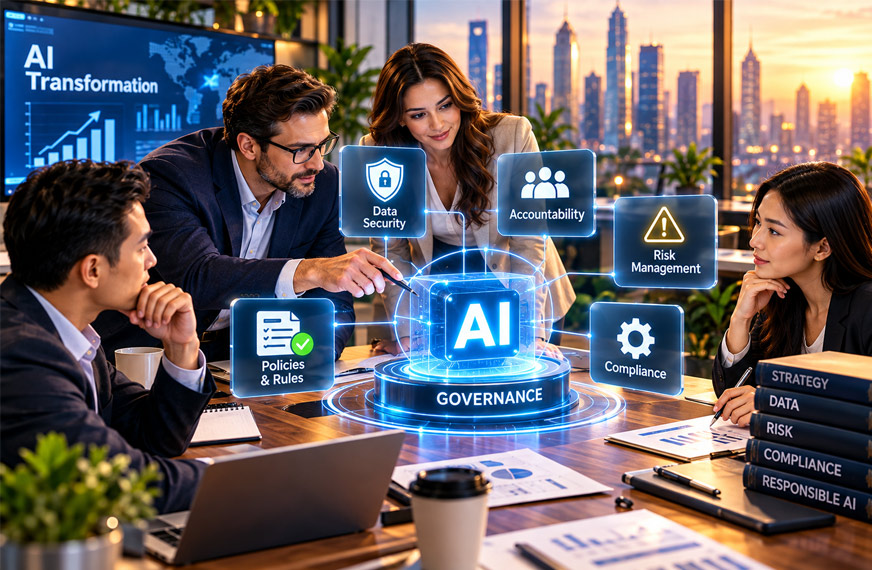
This is the main idea behind “AI transformation is a problem of governance.” This guide explains what the phrase means, why AI governance matters, and how businesses can manage AI in a practical way.
What Does “AI Transformation Is a Problem of Governance” Mean?
The phrase means that AI transformation is not only about technology.
A company may have a powerful AI model and skilled developers. It may still struggle to use AI safely across the business.
AI governance is the set of rules, roles, processes, and controls used to manage AI. It covers how AI is approved, developed, used, monitored, changed, and eventually retired.
A simple way to understand it is:
Technology tells a company what AI can do. Governance decides what AI should be allowed to do.
For example, an AI agent may be able to read customer files and send emails. This does not mean it should be allowed to do both without limits.
The business must decide what information the AI can access, what actions it can take, when a person must approve its work, and who is responsible for the results.
Governance is not the only challenge. AI projects can also fail because of poor data, weak planning, bad training, unsuitable technology, or unrealistic goals.
AI Adoption vs. AI Transformation
AI adoption and AI transformation are not exactly the same.
If an employee uses AI to improve an email, that is AI adoption. Giving workers approved AI tools for writing or research is also adoption.
AI transformation goes much further.
It happens when AI starts changing how a company works. It can change jobs, workflows, customer service, research, coding, sales, and decision-making.
For example, using AI to improve a customer service reply is a simple use.
Allowing AI to access customer records and answer customers automatically is much more serious. The system may handle private information and communicate directly with real people.
This creates questions about security, accuracy, data access, monitoring, and responsibility.
The more AI becomes part of normal business work, the more important governance becomes.
Why AI Transformation Becomes a Governance Problem
Testing a small AI tool can be easy. A team may test a chatbot, use an API, or create a simple AI workflow.
Using the same system across a business is harder.
A production AI system may need approved data, security checks, legal review, monitoring, stable workflows, and a clear owner.
The company also needs a plan for what happens if the system stops working correctly.
For example, imagine AI gives a customer incorrect financial information.
The model may come from an outside company. Developers may have built the system around it. A product team may have launched it. Another department may use it.
Who is responsible for the mistake?
Governance helps answer this question.
It also decides who can approve AI, what risks are acceptable, when people must check AI results, and when a system should be stopped.
A better AI model cannot solve all these problems. Even a powerful model needs rules and limits.
Decision Rights and AI Accountability
Decision rights explain who has the authority to make important choices about an AI system.
A company should know who can approve the system, who owns its business results, and who can stop or change it when there is a problem.
Different teams can have different roles.
A business owner may decide what the AI should achieve. Data teams can control access to information. Security teams can check technical protections. Legal and compliance teams can review uses that may create legal risks.
Company leaders may need to make final decisions about larger risks.
Clear responsibility is especially important when AI is used in areas such as hiring, lending, insurance, pricing, fraud detection, or procurement.
Every important AI system should have a clear owner.
That person does not need to do everything. Other teams can manage security, development, testing, and legal checks. But everyone should know who is responsible for the system’s business use.
Clear decision rights can also save time. Teams know who must approve each part of a project instead of arguing about responsibility later.
Data Governance and AI Security
AI needs data to work well.
A business should know what data an AI system uses, where that data comes from, who can access it, and whether it should be used for that purpose.
This information may include customer records, emails, contracts, private code, employee information, financial records, and internal documents.
Not every AI tool should have access to all company information.
A useful rule is simple: AI should not automatically get more access than the people using it.
Businesses also need rules about what employees can put into outside AI tools.
For example, an employee could accidentally paste customer details, private code, contracts, or business plans into an unapproved AI service.
Good data governance should cover data access, quality, source, storage, retention, and allowed uses.
Businesses should also understand how outside AI companies store and use their information.
AI can also expose old data problems. Weak security, poor access controls, and badly organized information may already exist.
Connecting AI to those systems can make the problems more serious.
Shadow AI and AI Sprawl
Shadow AI means workers are using AI tools that the company has not approved or properly reviewed.
Employees may not be trying to break the rules. They may simply find an AI tool that helps them work faster.
Problems can start when private company information is entered into an unapproved service.
This may create security, privacy, compliance, confidentiality, and intellectual property risks.
Another problem is AI sprawl.
Different departments may create their own AI accounts, agents, assistants, and automated workflows. Over time, a company may have many AI systems that management does not fully know about.
Banning every outside AI tool may not solve the problem.
A better approach is to give employees approved tools, simple rules, useful training, and an easy way to request new AI services.
Businesses can also keep an AI inventory.
This can record the system’s name, owner, vendor, purpose, data source, risk level, and review date.
The goal is not extra paperwork. The goal is to know which AI systems are being used.
Why Traditional IT Governance Is Not Enough
Normal IT governance is still important.
Businesses still need cybersecurity, access controls, change management, reliable systems, and other technology rules.
But AI creates some new problems.
Traditional software normally follows written code and set instructions. AI can give less predictable results.
Its behavior may change because of different prompts, new data, new users, or updates from the AI provider.
Generative AI can also give incorrect information. These incorrect answers are often called hallucinations.
Other concerns include private information, output quality, and knowing where AI-generated content came from.
An AI system may also perform differently after it is launched.
This means AI governance cannot stop after approval.
The NIST AI Risk Management Framework uses four main functions: Govern, Map, Measure, and Manage.
These ideas support AI risk management across the full lifecycle, from planning and development to monitoring and retirement.
Generative AI and Agentic AI Governance
Generative AI can create text, code, images, summaries, and other content.
Its answers can sometimes look correct even when they contain mistakes.
Businesses therefore need rules for checking important AI output. They also need rules for private information, intellectual property, and human review.
Agentic AI creates additional concerns.
A normal chatbot mainly answers questions. An AI agent may be able to search databases, use software, create files, update records, send messages, call APIs, or start workflows.
The question changes from:
“What can AI say?”
to:
“What can AI do?”
This makes permissions very important.
Businesses should decide which systems an AI agent can access and which actions it can perform.
Some simple actions may happen automatically. More important actions may require approval from a person.
Audit logs can record what an AI agent does. Monitoring can help find unusual behavior. Businesses should also have a way to stop an agent when needed.
The more power an AI system has, the more carefully that power should be controlled.
Risk-Based AI Governance
Not every AI system has the same level of risk.
An AI tool that improves an internal email is very different from AI used for hiring, lending, insurance, or other important decisions.
Businesses can therefore use risk-based AI governance.
Low-risk tools may only need simple rules and approved data.
Medium-risk systems may need an owner, access controls, testing, documentation, and logs.
High-risk systems may need stronger testing, human review, legal checks, and regular monitoring.
This helps businesses avoid using the same heavy approval process for every AI tool.
More control can be added when the possible harm is greater.
Human Oversight and Control
Human oversight means a person can review, correct, question, or stop an AI system when needed.
This is especially important when AI affects employees, customers, money, safety, or other serious matters.
Human review should be meaningful.
A worker who only clicks an “approve” button without checking the result is not providing strong oversight.
The reviewer should understand the task, have enough information, and be able to reject or change the AI result.
Businesses should decide when human approval is required before launching an AI system.
They should also have a clear process for reporting problems and stopping unsafe or unreliable AI.
The NIST AI Risk Management Framework
The NIST AI Risk Management Framework, also called the AI RMF, helps organizations understand and manage AI risks.
It has four main functions:
- Govern: Set rules, responsibilities, and accountability.
- Map: Understand the AI system, its purpose, users, and risks.
- Measure: Test and check the system and its risks.
- Manage: Decide which risks matter most and take action.
These functions work together.
The framework also covers areas such as reliability, safety, security, privacy, transparency, explainability, accountability, and fairness.
An important idea behind the framework is that AI risk management should continue after launch.
AI Governance and Regulation
Governments are creating more rules for artificial intelligence.
The EU AI Act is an important example. It uses a risk-based system, with stronger requirements for some higher-risk uses of AI.
Certain transparency requirements under the EU AI Act apply from August 2, 2026. These include rules related to some direct AI interactions and certain AI-generated or changed content.
Other parts of the law have different dates.
The rules that apply to a business can depend on the AI system, how it is used, its risk level, the industry, and the country.
Following the law is also not the same as having complete AI governance.
A company may meet legal requirements but still need stronger internal rules for security, quality, customer protection, or business risk.
How to Build an AI Governance Framework
A business can start with a simple question:
Where are we already using AI?
The company should create a list of its AI systems.
This can include AI developed inside the business, outside AI services, AI features inside other software, and known Shadow AI.
Each important system should have an owner.
The business should record what the system does, what information it uses, and how risky its use may be.
Teams should also know who can approve data access, security controls, legal reviews, and final deployment.
Controls can then be added based on risk. These may include testing, documentation, data limits, human review, vendor checks, monitoring, and logs.
The company also needs a clear process for AI incidents.
Employees should know how to report a problem, who will investigate it, and who can stop the system.
AI governance should be part of normal business work. It should not exist only in a policy document.
Governance by Design
Governance by design means adding important controls while an AI system is being built.
For example, access controls can limit the information AI can see.
Audit logs can record important actions.
Human approval steps can stop sensitive actions from happening automatically.
Teams can also record the AI system’s purpose, owner, data sources, limits, test results, and monitoring needs during development.
Adding these controls early is usually easier than trying to add them after the system is already being widely used.
Monitoring AI After Deployment
AI governance continues after launch.
An AI system’s performance can change over time.
New data may affect results. Employees may use the system in unexpected ways. The AI provider may update its model. Costs may also rise as usage grows.
Businesses should monitor the measures that matter for each system.
These can include accuracy, output quality, model drift, costs, complaints, incidents, and human overrides.
Important changes may also require another review.
For example, connecting an AI agent to a new database or giving it more permissions may create new risks.
Businesses should also have a process for retiring AI systems that are no longer safe, useful, supported, or suitable.
How Governance Helps AI Move From Pilot to Production
A successful AI test does not always mean the system is ready for the whole company.
A pilot may have a small number of users, clean data, and close technical support.
Real business use is more complicated.
A production system may need to handle more users, more data, security requirements, legal rules, and real mistakes.
A clear governance process makes this easier.
Teams know what tests are required, what documents are needed, who approves the system, and how it will be monitored after launch.
This can make moving AI from testing to production more predictable.
Benefits of Strong AI Governance
Good AI governance can help a company keep better control over its AI systems.
Main benefits include:
- Clear ownership and responsibility.
- Better protection of sensitive information.
- Better visibility into AI use.
- Clearer approval processes.
- Earlier detection of problems.
- Better incident response.
- Stronger human control over important decisions.
- Better teamwork between business, IT, security, legal, and compliance teams.
- An easier path from AI testing to wider business use.
Governance cannot prevent every AI mistake.
It can make problems easier to find, understand, and manage.
Challenges and Drawbacks of AI Governance
AI governance can create problems when it becomes too complicated.
If a simple AI experiment needs months of approval, employees may avoid the official process.
Too much paperwork can also slow useful work.
Governance requires time and money. Businesses may need resources for testing, training, security checks, documentation, monitoring, and incident management.
Another challenge is that AI changes quickly.
Models, tools, laws, and business uses can change. A policy that works today may need to be updated later.
For this reason, governance should be practical.
Simple, low-risk AI can have simple controls. Higher-risk AI should receive stronger checks.
Is Governance the Only AI Transformation Challenge?
No.
Governance is important, but it is only one part of AI transformation.
AI projects can also fail because of poor data, weak planning, unclear goals, unsuitable technology, or unrealistic expectations.
Employee training also matters.
Workers may not know how to use new AI tools correctly. Some teams may also resist new workflows.
Business and technical teams may have different goals or fail to communicate clearly.
Some tasks may simply not be good choices for AI automation.
So the phrase “AI transformation is a problem of governance” should not mean that governance explains every AI problem.
The main lesson is that technology alone is not enough.
AI Governance for Small Businesses
Small businesses also need basic AI governance.
A marketing agency may use AI to create content. An online store may use an AI chatbot. A recruitment company may use AI to review applications. A publisher may use AI for research or writing support.
Small companies do not normally need a large AI committee.
Simple rules may be enough.
The business should know which AI tools employees use, what information can be entered into them, who checks important output, and who is responsible.
As AI use grows, the rules can become more detailed.
The goal is control, not unnecessary paperwork.
Practical AI Governance Checklist
Before using AI more widely, a business should ask:
- Do we know which AI tools and systems are being used?
- Does every important system have an owner?
- Do we know why each AI system is being used?
- Do we know what data it can access?
- Have we checked its level of risk?
- Are its permissions appropriate?
- Does important work receive human review when needed?
- Are important AI actions recorded?
- Is the system monitored after launch?
- Can employees easily report problems?
- Is there a process for handling AI incidents?
- Can the system be stopped or suspended?
- Are major updates and permission changes reviewed?
- Can old or unsuitable AI systems be retired?
The checklist does not replace proper governance.
It simply helps businesses check whether the most important controls are in place.
Bottom Line
AI transformation is a problem of governance because successful AI use requires more than a powerful model.
Businesses need clear ownership, data rules, decision rights, risk controls, human oversight, and regular monitoring.
Good governance should not create paperwork without a reason.
Its purpose is to make clear what AI is doing, what it can access, what it is allowed to do, and who is responsible for it.
Businesses should not only ask:
“What can this AI do?”
They should also ask:
“Who controls it, what are the rules, and what happens if something goes wrong?”
Frequently Asked Questions
What does “AI transformation is a problem of governance” mean?
It means businesses need clear rules and responsibility when using AI. Technology alone is not enough.
What is AI governance?
AI governance is a set of rules for how a business uses and controls AI safely.
Why is AI governance different from IT governance?
AI can give changing or wrong results. It needs extra controls for data, risks, and human review.
What is Shadow AI?
Shadow AI is when employees use AI tools that their company has not approved.
Why does agentic AI need stronger governance?
AI agents can access systems and take actions. They need clear limits, monitoring, and human control.
Does AI governance slow innovation?
Poor governance can slow work. Simple rules can help businesses use AI safely without unnecessary delays.
Do small businesses need AI governance?
Yes. Small businesses should know which AI tools are used, what data they access, and who checks their work.
What are the first steps for AI governance?
List the AI tools being used, assign owners, check risks, set data rules, and monitor important systems.
Explore More:
Finelo Reviews 2026: Features, Pricing, Complaints, and Safety

