
Platform Event Trap is a technical term used in server management and cybersecurity. In server management, it is an alert about a hardware or system problem. In cybersecurity, some articles use the term for a process that finds security risks and takes action automatically.
These systems help IT teams find problems, protect software, and respond to security threats. This article explains what Platform Event Trap means, how it works, where it is used, and its main benefits.
What Is a Platform Event Trap?
In cybersecurity, Platform Event Trap can describe a process that checks important activities and takes action when they break security rules.
For example, a company may require approval before releasing new software. If someone tries to release it without approval, an automatic security check can stop the release.
This type of security does more than send warnings. It can block unsafe activity, pause a process, or ask someone to review it.
Companies can create these controls using security tools, cloud services, and automation software.
However, Platform Event Trap is not the official name of one cybersecurity product. It is also an established technical term used in IPMI server management.
Platform Event Trap Meaning in Different Technologies
Platform Event Trap can mean different things depending on the technology being discussed.
Platform Event Trap in IPMI Server Management
In server management, Platform Event Trap (PET) is a type of alert used with the Intelligent Platform Management Interface (IPMI).
IPMI helps IT teams check and manage server hardware.
A Platform Event Trap sends information about certain hardware or firmware events through an SNMP trap. These events may involve power problems, hardware sensors, or other important system changes.
A Baseboard Management Controller (BMC) helps manage these alerts. It works separately from the main operating system, so some hardware checks can continue even when the operating system is not running.
This is the established technical meaning of Platform Event Trap.
Platform Event Trap in Cybersecurity
In some cybersecurity articles, Platform Event Trap describes a security process that responds to important events.
For example, a security tool may find an exposed password, an unsafe cloud setting, or a software release without approval.
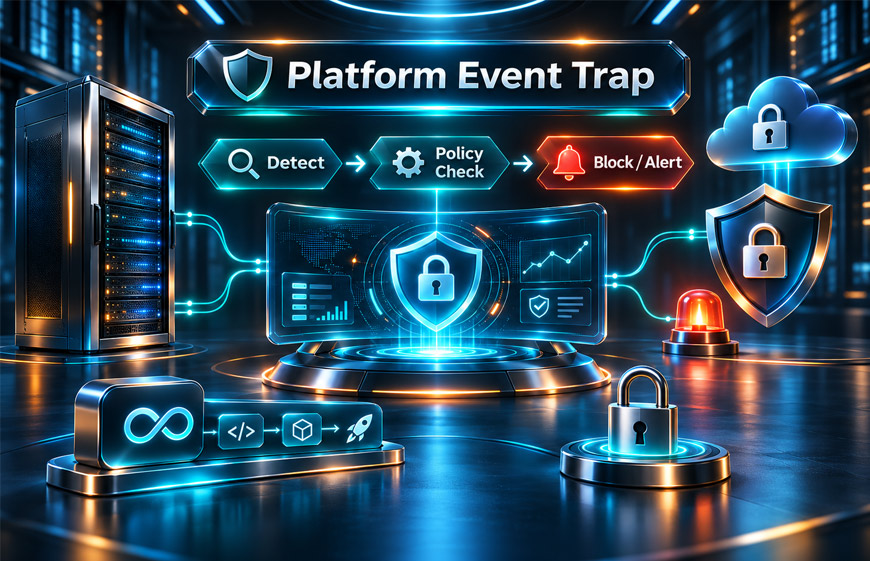
The system checks the event against security rules. It may then stop the activity, send an alert, or ask for approval.
This approach is called event-driven security.
However, Platform Event Trap is not a widely accepted official name for this cybersecurity process.
Platform Event Trap and Salesforce Platform Events
Salesforce uses Platform Events to share information between applications and automated processes.
Some online articles use the phrase Platform Event Trap when discussing problems with these events.
Common problems include receiving the same event more than once, missing messages, failed processing, or events arriving in an unexpected order.
However, Platform Event Trap is not an official Salesforce feature or error name.
These problems are related to event processing, not IPMI hardware alerts.
How Does a Platform Event Trap Work?
In event-driven cybersecurity, the process starts when something important happens in a system.
This could be a code change, a software release, a cloud setting update, or an attempt to access a protected resource.
A connected security tool receives information about the activity.
The system then checks that information against its security rules.
If the activity follows the rules, it can continue. If it breaks a rule, the system may stop it, pause it, or send an alert.
For example, a developer may accidentally add a private API key to a code update.
A security scanner finds the possible key and sends an alert. A connected security rule may stop the code from being approved until the problem is checked.
If the key has been exposed, an authorized system may also help replace or disable it.
The system records the event and the action taken so the security team can review it later.
The process follows four simple steps: detect the event, check the rules, make a decision, and take action.
Key Components of a Platform Event Trap
An event-driven security system needs several parts to work correctly.
Event Sources
An event source is where an activity happens.
Common examples include Git repositories, cloud platforms, CI/CD pipelines, and identity systems.
For example, a Git repository may report a new code change. A cloud platform may report an update to its security settings.
The information must be correct so the security system can make the right decision.
Event Listeners and Integrations
Event listeners receive information about activities taking place in connected systems.
They may use webhooks or other software connections.
For example, a webhook can inform a security tool when someone starts a deployment.
If the information arrives late or does not arrive at all, the security system may not respond correctly.
Policy Engine
A policy engine checks activities against security rules.
For example, a company may require approval before new software can be released.
The policy engine checks whether that approval exists.
It may also check access permissions, security test results, or software verification requirements.
Clear rules help prevent mistakes and unnecessary blocking.
Enforcement System
The enforcement system takes action when an activity breaks a security rule.
It may stop a build, block a code update, pause a deployment, or request approval.
Some systems can also start an investigation or a process to protect exposed credentials.
The response should depend on how serious the problem is.
Audit Logs
Audit logs record important activities and security decisions.
They show what happened, which rule was checked, and what action was taken.
These records help security teams investigate problems and understand why an activity was blocked.
They also help teams improve security rules over time.
Common Events That Trigger a Platform Event Trap
Event-driven security systems can respond to different activities.
One common example is an exposed API key or password. If a scanner finds private information in source code, the system may stop that code from being approved.
Another example is a code change without permission. A company may block changes that do not have the required approval.
Software releases can also trigger security checks. If a build fails an important test, the deployment may be stopped.
Cloud changes are another example. A system may send an alert when someone changes firewall settings or makes private storage publicly available.
Unusual service account activity may also require review.
Not every event needs to be blocked. Some only need an alert or approval from a security team.
Platform Event Trap Examples
These examples show how event-driven security can work.
Exposed API key: A developer accidentally adds an API key to source code. A scanner finds it and stops the code change. The team checks the key and replaces it if needed.
Unauthorized deployment: Someone tries to release software without permission. The system checks the approval status and stops the release.
Unverified software: A software build fails an important verification check. The system prevents it from reaching production.
Unsafe cloud settings: Someone changes private cloud storage to allow public access. The security system reports the change and may start a response.
Unusual account activity: A service account tries to perform an action outside its approved permissions. The system may block the request or ask for review.
These are examples of possible security processes, not reports of incidents at specific companies.
Platform Event Trap in CI/CD Pipelines
CI/CD stands for Continuous Integration and Continuous Delivery or Deployment.
It helps developers build, test, and release software automatically.
These processes save time, but security mistakes can also move through them quickly.
Event-driven security controls can check activities at different stages.
When developers submit code, the system may look for exposed credentials, missing approvals, or failed security tests.
During the build process, it can check software files and dependencies.
Before deployment, the system may confirm that all required tests and approvals are complete.
If an important check fails, the release may be stopped.
This supports DevSecOps, which means including security in software development and operations.
CI/CD security is important because automated pipelines may have access to private code, credentials, cloud services, and production systems.
If someone gains control of a powerful pipeline account, they may be able to access important resources. Security checks and limited permissions help reduce this risk.
Platform Event Trap in Cloud Security
Cloud platforms help businesses manage servers, storage, databases, networks, and applications online.
These systems change regularly as users add resources or update settings.
Event-driven security can help detect changes that break company rules.
For example, a business may require its cloud storage to remain private.
If someone changes the settings and makes it publicly available, the security system can send an alert.
Some systems can also restore the approved settings automatically. However, automatic changes need careful testing because they may affect normal services.
Another common issue is cloud configuration drift.
This happens when cloud settings become different from the approved setup.
For example, someone may change a firewall rule without permission.
Event-driven security can help teams find these changes earlier.
These controls can also work with cloud monitoring, identity management, and infrastructure-as-code tools.
Platform Event Trap and Secret Security
In software development, secrets are private details that allow systems to access other services.
Examples include passwords, API keys, access tokens, certificates, and signing credentials.
Applications need these details to connect with other systems.
However, exposing them can create security risks.
Secrets may accidentally appear in source code, build logs, configuration files, or software packages.
Security scanners can find possible exposures.
An automated security control may then stop the affected code from moving forward until the problem is reviewed.
Removing a secret from the latest code does not always solve the problem.
It may still exist in older code versions, logs, saved files, or copied information.
If the secret may have been exposed, the company may need to replace or disable it.
Rotation means replacing an old credential with a new one.
Revocation means making the existing credential unusable.
These actions help protect systems when private credentials may have been exposed.
Platform Event Trap and Non-Human Identity Security
Not every account in a computer system belongs to a person.
Applications, bots, service accounts, and automated tools also use accounts to access systems.
These are called non-human identities.
For example, an automated deployment tool may use a service account to upload software or manage cloud resources.
These accounts sometimes have important permissions.
If their credentials are stolen or misused, someone may gain access to protected systems.
Event-driven security controls can check activities performed by these accounts.
For example, if a service account tries to access something outside its allowed permissions, the system may stop the request or ask for approval.
One important security rule is least privilege.
This means giving an account only the permissions it needs to do its work.
Companies should also review their automated accounts, protect credentials, and remove access that is no longer needed.
Not every unusual action means an attack. Security systems need enough information to tell normal activity from a possible threat.
Platform Event Trap vs. Traditional Security Monitoring
Traditional security monitoring and event-driven security enforcement have different jobs.
Security monitoring collects information about system activities. It helps teams find unusual behavior and receive alerts.
Event-driven enforcement can take action when an activity breaks a security rule.
For example, monitoring software may warn a team about a deployment without approval.
An automated security control may stop that deployment until approval is given.
However, not every warning should cause an automatic block. Some problems need human review.
Both approaches are useful. Monitoring helps teams understand problems, while automated controls can stop certain unsafe actions quickly.
Platform Event Trap vs. Other Security Technologies
Platform Event Trap is often discussed with other security technologies.
These tools do different jobs, but they can work together.
| Technology | Main Purpose |
|---|---|
| Platform Event Trap | Connects events with security rules and actions |
| Webhooks | Send information when something happens |
| SIEM | Collects and checks security information |
| SOAR | Helps automate security responses |
| Policy-as-Code | Uses computer-readable security rules |
A webhook sends information from one system to another when an event happens.
SIEM stands for Security Information and Event Management. It helps security teams collect and review information from different systems.
SOAR stands for Security Orchestration, Automation, and Response. It helps connect tools and automate security tasks.
Policy-as-code allows companies to write rules that software can check automatically.
A company may use several of these technologies together to detect security risks and respond to them.
Security Benefits of Platform Event Traps
The main benefit of event-driven security is faster action.
When a security problem is found, the system can respond without waiting for someone to read an alert.
This may help stop unauthorized deployments, unsafe code changes, and risky cloud settings.
It can also help protect private credentials.
For example, if a scanner finds an exposed API key, an automated control may stop the affected code change until the key is checked.
Another benefit is consistency. The same security rules can be applied across different projects and systems.
Audit logs also help teams understand what happened during an incident.
Automation may reduce manual work for repeated security checks.
However, these benefits depend on accurate information, clear rules, and working tools.
Automated security cannot stop every cyberattack.
Risks and Limitations of Platform Event Traps
Automated security systems can also make mistakes.
One common problem is a false positive. This happens when the system treats a safe activity as a security risk.
For example, an incorrect rule may stop a normal software release.
Missing information can also cause problems. If the system does not receive an important event, it may fail to respond.
Events may arrive late, appear more than once, or reach systems in the wrong order.
Connected tools may also stop working or lose required permissions.
Some automated actions can create serious problems. For example, disabling an important account or changing cloud settings incorrectly may interrupt business services.
Companies must also decide what happens when a security check is unavailable.
Fail-open means the activity can continue even when the check fails. This may prevent delays but can increase security risk.
Fail-closed means the activity must stop until the check works again. This offers stronger protection but may delay normal work.
The right choice depends on the system and the possible risks.
How to Implement a Platform Event Trap
Creating an event-driven security process requires planning, clear rules, and testing.
1. Identify Important Security Risks
Start by finding activities that could cause serious problems.
These may include exposed credentials, unauthorized releases, unsafe cloud changes, or unusual access requests.
Focus on situations where a quick response can reduce the risk.
Not every event needs automatic blocking.
2. Choose Reliable Event Sources
Choose systems that provide the information needed for security checks.
These may include Git repositories, CI/CD pipelines, cloud platforms, and identity systems.
Make sure the information is accurate and complete.
Incorrect data can lead to incorrect security decisions.
3. Create Clear Security Policies
Write rules that explain which actions are allowed and which need approval.
For example, a rule may require permission before a production release.
Another rule may stop code changes containing exposed credentials.
Each rule should have a clear purpose and response.
4. Connect Security Tools
Connect the systems that detect events, check rules, and take action.
These connections may use webhooks, scanners, policy engines, or automation tools.
Give each tool only the permissions it needs.
Too much access can create more security risks.
5. Test Before Enforcing
Test security rules before allowing them to block important work.
One useful method is audit mode.
In audit mode, the system records what it would block without stopping the activity.
Teams can review these results and correct mistakes.
They should also test what happens when events are missing or connected tools fail.
6. Enable Enforcement Gradually
Start with simple rules that address serious risks.
For example, a company may first block software releases that do not have approval.
Add more rules after testing their results.
There should also be a safe way to review and approve special cases.
7. Monitor and Improve
Security rules need regular checks.
Review audit logs, blocked activities, failed actions, and approved exceptions.
Update the rules when software systems or company requirements change.
Regular testing helps keep the process reliable.
Platform Event Trap Best Practices
Good event-driven security depends on accurate information and clear rules.
Companies should use reliable event sources and avoid creating rules that block too many normal activities.
Automation tools should only receive the permissions they need.
Security rules and settings should also be protected from unauthorized changes.
Testing is important before automatic blocking is enabled.
Every major security action should be recorded in an audit log.
Companies should also decide who can approve exceptions or change security decisions.
There should be a safe recovery process when automation makes a mistake.
For example, if a normal software release is blocked incorrectly, the team should be able to review the problem and restore the process safely.
Important actions, such as disabling accounts or changing production systems, need extra care.
Human approval is useful when the situation is unclear or the action may cause serious problems.
Platform Event Traps and Cybersecurity Standards
The cybersecurity meaning of Platform Event Trap is connected with several established security practices.
However, it is not an official security control created by NIST or OWASP.
The NIST Cybersecurity Framework 2.0 helps organizations manage cybersecurity risks. It covers finding risks, detecting problems, responding to incidents, and recovering from them.
NIST SP 800-53 provides security and privacy controls for areas such as monitoring, access control, and incident response.
The NIST Secure Software Development Framework (SSDF) provides guidance for improving security during software development.
OWASP publishes information about application security, credentials, software supply chains, and CI/CD risks.
Event-driven security controls can support these practices by checking important activities and responding to certain violations.
They can also support Zero Trust.
Zero Trust means access should be checked based on identity, permissions, and other important details. A system should not automatically trust an activity simply because it comes from a familiar source.
These security frameworks provide useful guidance, but they do not require a product specifically called Platform Event Trap.
Who Should Use Platform Event Trap Security Controls?
Event-driven security controls can help businesses that use automated software and cloud systems.
Software development teams can use them to check code changes, builds, and releases.
DevOps and DevSecOps teams can use them to improve security in CI/CD pipelines.
Cloud teams may use them to find unsafe settings or unexpected changes.
Security teams can connect important alerts with automatic responses.
Companies with many service accounts or automated systems may also use these controls to check account activity.
They are especially useful when waiting too long to respond could make a security problem worse.
However, small teams may not need complex automation.
Basic security scanners, code approval rules, and monitoring tools may be enough for some businesses.
The main question is whether automatic action would help reduce an important security risk.
Common Problems and Troubleshooting
Event-driven security systems can face different problems. Finding the cause helps teams choose the correct fix.
Legitimate Actions Are Being Blocked
Sometimes a normal code change or software release is blocked.
This may happen because a rule is too strict or the system reports a false positive.
Check the audit logs to find which rule caused the block.
Review the rule and correct it if needed.
Test the updated rule before using it again.
Security Events Are Not Detected
Sometimes a security event happens, but the system does not detect it.
This may be caused by missing permissions, incorrect settings, or broken connections.
Check whether the original system created the event.
Then review the event listener, connected tools, and security rules.
Testing with a known event can help find the problem.
Automated Responses Fail
A system may find a security problem but fail to complete the required action.
For example, a security tool may not have permission to stop a deployment.
Check the error message, tool permissions, and connection status.
Also check whether part of the action was already completed.
Repeating an unfinished action without checking its result may cause more problems.
Security Rules Cause Delays
Some security checks may slow down builds or software releases.
This can happen when a connected tool responds slowly or an important check takes too long.
Review the time taken by each check.
Find the slow process and improve it where possible.
Do not remove important security checks only to make releases faster.
Duplicate or Delayed Events
Some systems may send the same event more than once.
Events can also arrive late or in the wrong order.
This may cause repeated alerts or unwanted actions.
Where possible, use event IDs to recognize information that has already been processed.
Automated actions should also be safe to repeat when the same event is received again.
Clear logs can help teams find and fix these problems.
Future of Event-Driven Security
Software development and cloud systems continue to use more automation.
This makes fast and reliable security checks increasingly useful.
Policy-as-code may become more common because it allows teams to manage security rules through software.
Cloud platforms and automated accounts also create more opportunities for event-based security.
Better event information can help systems make more accurate decisions.
AI-assisted security tools may also help teams review large amounts of data and find unusual activity.
However, AI results still need proper checks before they lead to important automated actions.
Human review will remain necessary for unclear events, serious incidents, and important security decisions.
The main goal is not to automate everything. It is to respond to security risks more accurately and safely.
Bottom Line
Platform Event Trap has an established meaning in IPMI server management. It is an alert used to report certain hardware or firmware events.
In some cybersecurity articles, the term also describes an event-driven security process that detects risky activities and responds using security rules.
These controls can help protect software releases, cloud systems, private credentials, and automated accounts.
Their main benefits include faster responses, consistent security checks, and better records.
However, automation needs accurate rules, reliable tools, regular testing, and human review to work properly.
Frequently Asked Questions
What is a Platform Event Trap?
In IPMI, it is a hardware or firmware alert. In cybersecurity, some articles use the term for a process that detects security risks and takes action.
How does a Platform Event Trap work?
In cybersecurity, it detects an event, checks security rules, and responds by blocking, pausing, or sending an alert.
Is Platform Event Trap a security tool?
Not exactly. In cybersecurity, it describes an approach that can use different security and automation tools.
What is Platform Event Trap in IPMI?
It is a server management alert that reports certain hardware or firmware events through an SNMP trap.
Can Platform Event Traps protect CI/CD pipelines?
Yes. Event-based security controls can help stop unsafe code changes, failed builds, and unauthorized deployments.
What are the main benefits of Platform Event Traps?
They can provide faster security responses, consistent checks, and useful records for investigations.
What are the risks of automated security enforcement?
Common risks include false positives, incorrect blocking, failed connections, and delays to important work.
What is the difference between Platform Event Trap and security monitoring?
Security monitoring finds problems and sends alerts. Automated enforcement can also stop or pause activities that break security rules.
Explore More:

